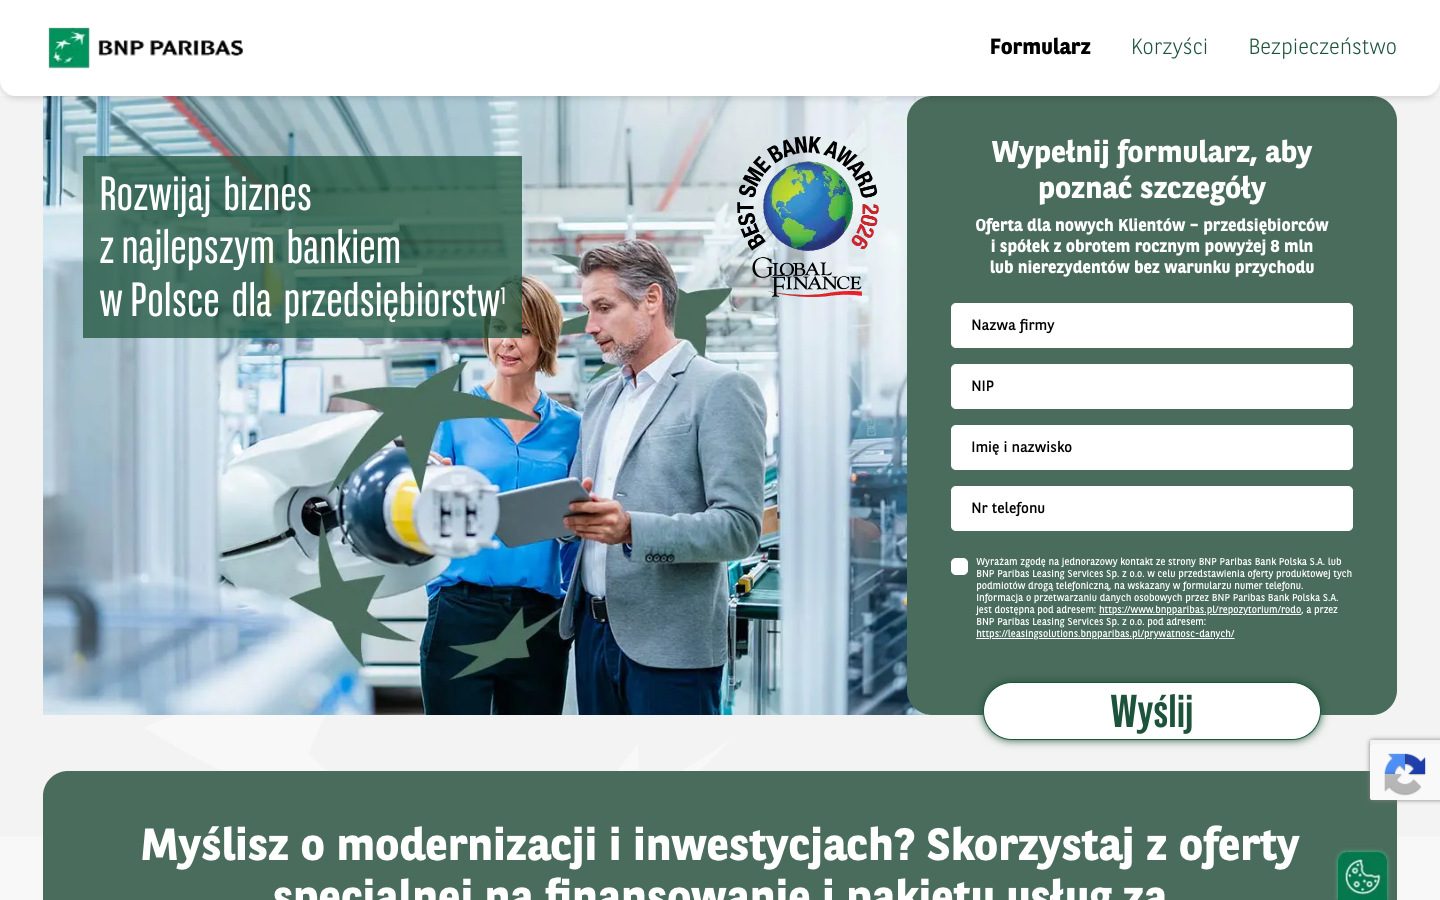
BNP Paribas - Profit Box
Production landing under lp.bnpparibas.pl/ofertaspecjalna/: form → SQLite → SMTP → weekly Excel reports and Bankier affiliation, deployed behind Hagen with basePath, CSP nonces, and CSRF.
Technologies
 Next.js
 React
 TypeScript
 Prisma
 SQLite
 Nodemailer
 reCAPTCHA
 Tailwind CSS
 PM2
?Challenge
Ship a conversion LP inside closed bank infrastructure with security audit (CSP without unsafe-inline), bot/CSRF protection, and Consent Mode.
✓Solution
Next.js App Router + proxy.ts (Basic Auth, CSP nonce, CSRF), Server Actions with reCAPTCHA v3, Prisma/SQLite, GTM/OneTrust, PM2 + local SSL tunnel.
Key decisions
Bank landing platform
Shared pattern with Axepta: proxy CSP/CSRF, Server Actions, Prisma, SMTP, GTM/OneTrust, PM2.
CSP-first frontend
Per-request nonces, strict-dynamic, no inline styles/scripts - built for bank security review.
Lead pipeline end-to-end
Validate → CSRF → reCAPTCHA → DB → mail; weekly XLSX export and thank-you attribution.
Results
Live on bank domain behind Hagen
Audit-ready CSP + lead hardening
Ops: healthcheck, Excel cron, DEV/PROD ENV